Why protecting employee badges, smart cards, and contactless credentials throughout their lifecycle is an essential part of modern identity security.
Identity security discussions have become increasingly sophisticated. Enterprises are investing in passkeys, multifactor authentication, zero-trust architecture, privileged access controls, and automated identity governance. Yet one part of the identity lifecycle is often treated as an afterthought: the physical credential after it has been issued.
Employee badges, smart cards, PIV cards, visitor credentials, and other contactless IDs remain essential in offices, government facilities, laboratories, healthcare environments, data centers, and industrial sites. They connect a person’s identity to doors, systems, restricted zones, and sometimes multiple authentication workflows.
Once those credentials leave the issuance desk, however, they enter a far less controlled environment. They may be carried in pockets, bags, or lanyards, left on desks, or exposed in elevators, public transport, restaurants, and shared workspaces.
That gap matters. Identity security does not end when a credential is successfully provisioned. It continues throughout the credential’s physical lifecycle.
Why Issuance Is Only the Beginning
Organizations typically apply strong controls when issuing a credential. The employee’s identity is verified, access rights are assigned, the card is encoded, and the credential is registered in an access-control system. In regulated environments, the process may involve additional approval, documentation, or biometric verification.
After issuance, responsibility often becomes fragmented.
The security team may manage access permissions. Facilities may manage doors and readers. HR may trigger onboarding and offboarding. Employees are expected to keep badges secure. Procurement teams may select holders, reels, clips, and other accessories based primarily on price or convenience.
Each function may work effectively on its own, but gaps can emerge when responsibilities are divided across different teams.
A 2026 study by the FIDO Alliance and HID illustrates the broader issue. Among 500 IT and cybersecurity decision-makers surveyed across the United States, Canada, the United Kingdom, France, and Germany, 94% said they were confident they could revoke an employee’s physical and digital access within 24 hours of departure. However, 35% reported experiencing delays or failures in doing so during the previous two years.
The lesson is not simply that offboarding needs improvement. Physical and digital identity should be managed as parts of the same continuous security process rather than as separate administrative tasks.
Physical Credentials Are Active Security Assets
An ID badge can look passive, but many modern credentials are active components of an organization’s security infrastructure.
Contactless smart cards may communicate with readers through RFID or NFC technologies. Some are used for physical access, while others support logical authentication or contain information that participates in broader identity systems. NIST’s FIPS 201-3 standard, for example, defines PIV cards as credentials used for authentication to both physical and logical resources and specifies contact and contactless interfaces.
This means a credential should be treated more like a security token than a simple piece of printed plastic.
That distinction changes the questions organizations should ask. Where is the credential stored when it is not in use? Can it be read unintentionally? Is sensitive information visible to unauthorized observers? Can the card easily become separated from its holder? What happens when it is lost, damaged, reassigned, or no longer required?
These are lifecycle questions, not just issuance questions.
The Risk of Unintended Contactless Reads
Contactless credentials are designed for convenience. A user presents a card near a compatible reader, allowing fast access without having to insert it into a device.
That convenience, however, also creates a need for controlled exposure.
Organizations should understand the technologies used in their badges, the frequencies involved, what information can be exchanged, and whether shielding is appropriate for their specific security requirements. RFID-blocking accessories can provide an additional physical control by limiting communication with a credential while it is stored. The user can then expose the card when an authorized read is required.
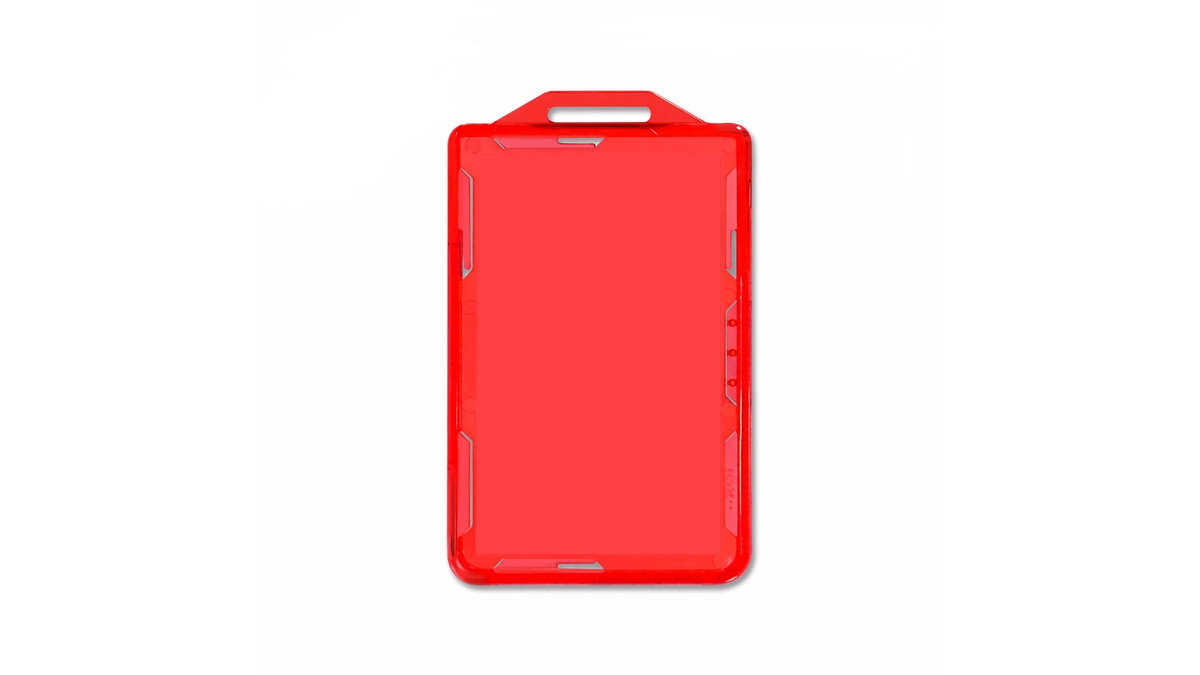
For organizations using compatible smart cards or PIV-style credentials, a shielded holder can serve as one component of a layered security approach. For example, the AC926-RFID Vertical Shielded Card Holder combines RFID shielding with a vertical dual-card format, allowing two standard CR80-size cards to be carried together while helping prevent unintended RFID reads when the cards are enclosed.
A holder does not replace technical security controls. Credential shielding should complement secure card technology, access policies, reader configuration, authentication requirements, monitoring, and user training.
Designing Security Around Daily Behavior
Security controls work best when they match the way people actually work.
An employee who taps a badge dozens of times per day may need a different carrying method from someone who uses a credential only to enter a building each morning. A technician wearing gloves may require a different setup from an office worker. A healthcare employee may prioritize quick access and hands-free movement, while a contractor may require a visibly distinct temporary credential.
This is why seemingly simple choices such as badge orientation, attachment method, card capacity, visibility, and release mechanism can influence security behavior.
If a protective solution is inconvenient, users may stop using it. If a badge holder makes scanning difficult, employees may begin carrying cards loose. If credentials are difficult to distinguish, visual checks can become less effective. If temporary badges look identical to permanent ones, employees and security personnel may have fewer visual cues for identifying unusual access.
Physical credential design should therefore be considered part of security usability rather than a purely administrative or purchasing decision.
Five Questions for a Better Credential Lifecycle
Organizations reviewing physical identity security can begin with five practical questions.
First, what happens immediately after issuance? Organizations should define how credentials are carried, protected, displayed, and stored rather than assuming that users will determine their own methods.
Second, which credentials use contactless technology? Not every badge requires shielding. Security teams should identify the technologies used in their cards and match protective measures to actual risks.
Third, who owns the physical credential lifecycle? Clear responsibility should cover issuance, permission changes, replacement, temporary use, lost-card response, offboarding, and destruction.
Fourth, how quickly can physical access be revoked? Deactivating a corporate account while leaving a building credential active creates an avoidable gap. Physical and digital offboarding workflows should therefore be coordinated.
Fifth, what happens to expired or returned credentials? Cards should not simply accumulate in drawers. Organizations need procedures for deactivation, collection, destruction, appropriate reuse, and documentation.
Closing the Credential Security Gap
As identity systems become more digital, physical credentials remain an important part of everyday access control. Employees still move between digital systems and physical spaces throughout the same workday, and the badge they carry may be connected to the same broader identity infrastructure that protects their devices, applications, and workplace access.
For this reason, issuing a credential should be viewed as the beginning of its security lifecycle, not the end of the process.
Organizations can strengthen credential security by reviewing how badges are carried and stored, identifying which contactless credentials require additional protection, establishing clear procedures for lost or expired cards, and ensuring that physical access is revoked at the same time as digital access.
None of these measures needs to be complicated. Their value comes from making credential protection consistent from issuance through daily use and, eventually, retirement.
As organizations continue investing in zero trust, passwordless authentication, and identity governance, physical credentials should remain part of the same security strategy. Effective identity protection depends not only on how credentials are created, but also on how they are handled, protected, and ultimately deactivated throughout their entire lifecycle.